HIPAA & PHI for AI
Does Zero Data Retention Satisfy HIPAA, and What a BAA Covers That ZDR Does Not
Zero Data Retention alone doesn't satisfy HIPAA's full legal requirements for vendors.
Priya Venkatasubramanian9 min read
Patient data sent to AI models requires a signed BAA from every service in the data path.
Zero Data Retention alone doesn't satisfy HIPAA's full legal requirements for vendors.
Organizations must redact patient data from LLM prompts before sending them to external providers.
Real-time cost tracking turns shared provider bills into actionable team spending data.
Seven criteria separate PII redaction tools that protect data before LLM submission.
One API enforces cost controls and security across multiple LLM providers.
Unified API access to multiple LLM providers without managing infrastructure yourself.
Finance and security leaders need these infrastructure controls to govern AI risk.
Federated identity ties every LLM request to a known user for automatic access control.
Compliance auditors demand individual attribution in AI logs, and most deployments lack it.
Routing-layer telemetry enables real-time, granular LLM spend tracking by team.
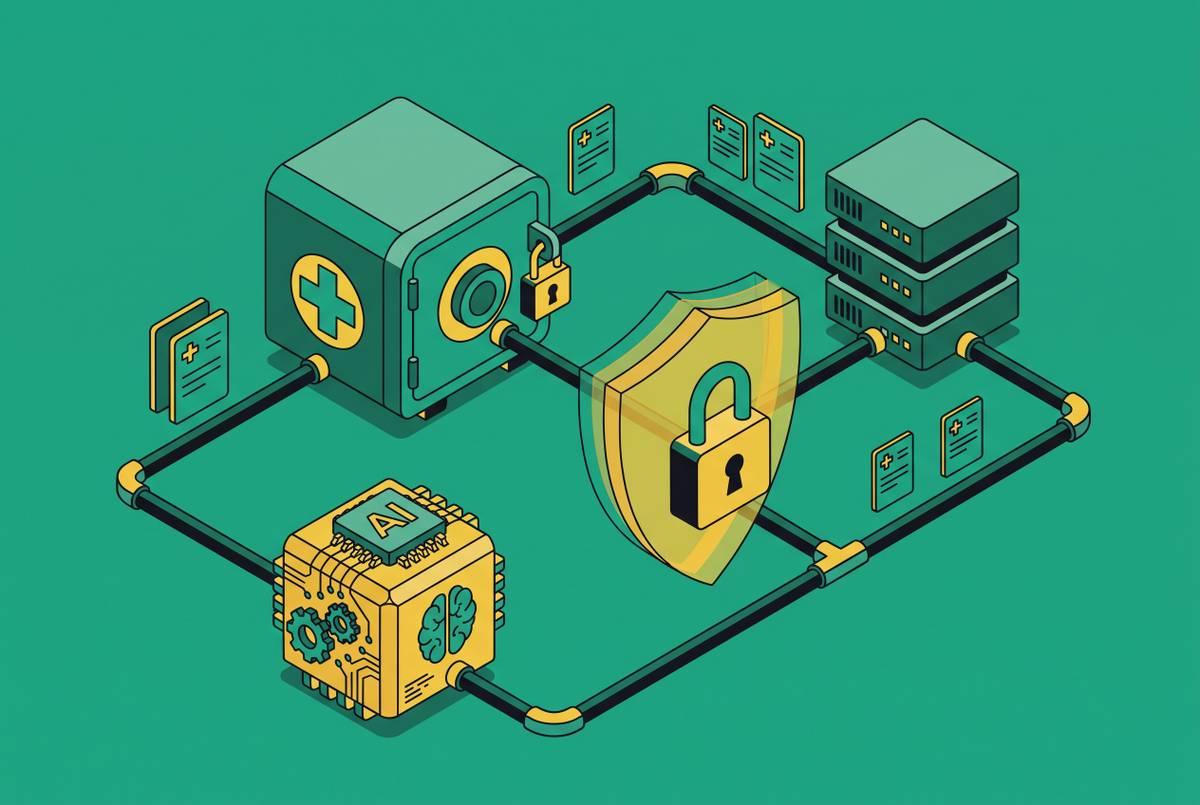
HIPAA compliance requires controls at every layer of an AI workflow, not just the model itself.